VAPT and penetration testing.
Scoped to UAE regulations.

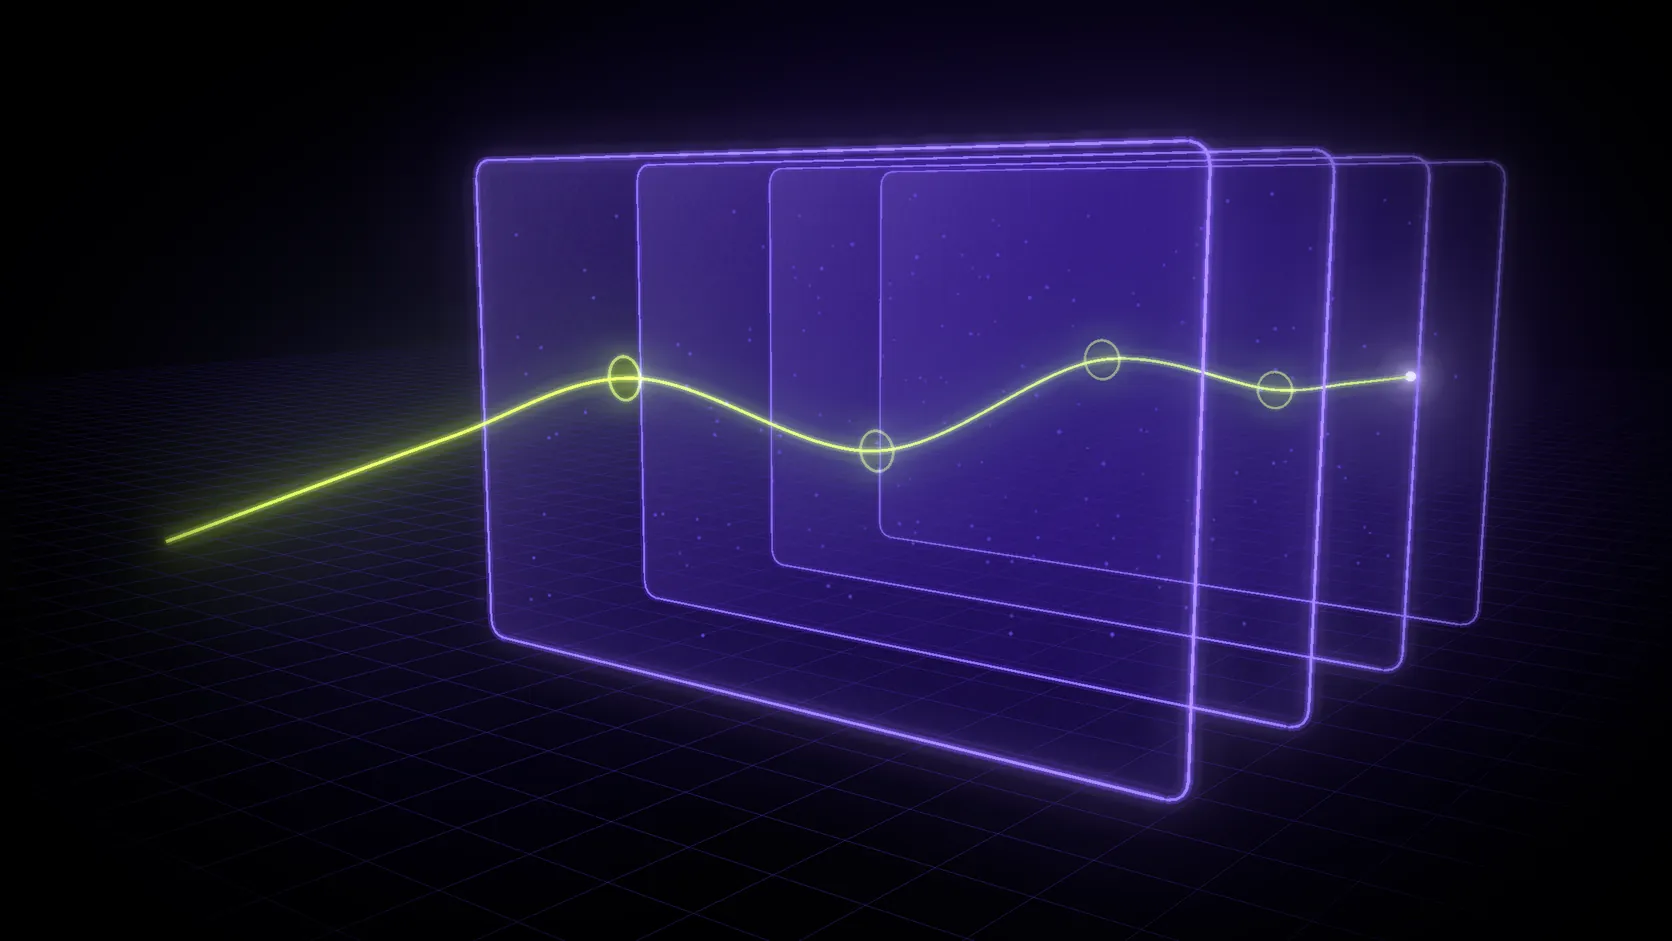
VAPT services by IrenicTech: four violet glass layers for web, mobile, network and cloud, scattered with dim scan marks, threaded by one lime line through a gap in each layer to the core, the way in a manual penetration test finds

The toolkit

The tools behind every VAPT engagement

  • Burp Suite
  • ZAP
  • Postman
  • Metasploit
  • Wireshark
  • Kali Linux
  • Trivy
  • Qualys
  • Hashcat

IrenicTech VAPT at a glance

Scanners find candidates. Testers find the way in.

VAPT is two jobs in one engagement. The vulnerability assessment sweeps the whole surface for known weaknesses: outdated components, exposed services, weak TLS, missing headers, misconfigured cloud resources. The penetration test is the part a scanner cannot do. A person takes those candidates, chains them, and proves which ones an attacker could actually use.

Most of what matters lives in the second half. Broken access control between two tenants, a password reset that can be replayed, an API that trusts an ID from the client, a mobile app that ships its secret key. None of these show up as a red line in a scan report. They show up when someone tries.

Our own team does the testing, end to end. You get every finding scored, reproduced and explained, a retest after you fix, and a signed letter you can hand to the customer or auditor who asked.

Productized engagements

Four VAPT engagements. Fixed scope, fixed price.

Pick the surface, or combine them. Each one is scoped in writing before testing starts, and each ends with the same report, the same retest and the same signed letter.

  • Web apps & APIs

    Web & API VAPT

    Logged out and logged in, every role, every endpoint in scope.

    • Tested against the OWASP Web Security Testing Guide and the OWASP Top 10
    • Authentication, session handling, access control between roles and tenants
    • REST and GraphQL APIs, including business logic a scanner cannot reason about

    Toolkit

    • Burp Suite
    • ZAP
    • Postman
    • sqlmap
    • Nuclei
    • ffuf
    Book a scoping call
  • iOS & Android

    Mobile App VAPT

    The app on the device and the API behind it, tested together.

    • Tested against the OWASP MASVS, on iOS and Android builds
    • Local storage, hardcoded secrets, certificate pinning and traffic interception
    • The backend API the app talks to, from the attacker's side of the phone

    Toolkit

    • MobSF
    • Frida
    • objection
    • jadx
    • Burp Suite
    Book a scoping call
  • Network & servers

    Network & Infrastructure VAPT

    External first, internal when the scope calls for it.

    • Discovery of exposed hosts, ports and services across your address ranges
    • Known vulnerabilities verified by hand, not copied out of a scanner
    • Weak protocols, default credentials and paths from one host to the next

    Toolkit

    • Nmap
    • Nessus
    • Qualys
    • Metasploit
    • Wireshark
    • Impacket
    • Hashcat
    Book a scoping call
  • AWS, Azure & GCP

    Cloud Configuration Review

    The misconfigurations that turn one leaked key into a breach.

    • Identity and access policies, public storage, network exposure and logging
    • Checked against the CIS Benchmarks for your cloud provider
    • Read-only access from you; nothing in your account is changed

    Toolkit

    • Prowler
    • ScoutSuite
    • Trivy
    • kube-bench
    Book a scoping call

What lands in your VAPT report

  • Executive summary

    One readable page for the person who signs off: what was tested, what was found, how serious it is, and what to fix first.

  • CVSS-scored findings

    Every finding rated with a CVSS score and vector, so severity is a standard number your auditor and your engineers both recognise, not our opinion.

  • Proof of concept

    Exact steps, requests and screenshots to reproduce each exploitable finding, so your team can confirm it in minutes instead of arguing about it.

  • Remediation guidance

    A specific fix for each finding, written for the stack you run, with references to the OWASP or CIS control it maps to.

  • Free retest

    Once your team has fixed the findings, we test them again at no charge and reissue the report with each one marked fixed or still open.

  • Signed attestation letter

    A signed letter stating the scope, the test dates and the outcome, for the enterprise customer, auditor or regulator who asked for proof.

What we test

Tested across the platforms you ship on

  • AWS
  • Microsoft Azure
  • Google Cloud
  • Kubernetes
  • Docker
  • Cloudflare
  • Swift
  • Kotlin
  • Flutter

Scan report vs penetration test

Why a scan report is not a pentest.

Both arrive as a PDF. Only one of them tells you how someone would actually get in, and whether your fix closed the door.

The default pattern

Scan and export

  • An automated scanner runs overnight and exports a long PDF of every possible issue.
  • Half the findings are false positives your engineers spend a week disproving.
  • Business logic flaws, access control between tenants and chained bugs never appear.
  • Severity is whatever the tool decided, with no context about your system.
  • Nobody checks whether the fixes worked; the next scan simply looks different.
  • The buyer who asked for a pentest reads it and asks for a real one.

How we test

IrenicTech VAPT

  • Automated scanning for coverage, then a person testing the surface by hand.
  • Every reported finding verified and reproduced before it reaches the report.
  • Access control, business logic and chained attacks tested deliberately.
  • Each finding scored with CVSS and explained in terms of your system.
  • A free retest confirms each fix, and the report is reissued to match.
  • A signed attestation letter the customer or auditor can actually accept.

When teams call us for VAPT.

  1. 01 · UAE

    A UAE regulator or government buyer asks for VAPT

    UAE frameworks such as the UAE Information Assurance standard, Dubai's DESC Information Security Regulation and ADHICS for Abu Dhabi healthcare expect regular vulnerability assessment and penetration testing. Tell us which one applies and we scope the test to it.

  2. 02 · Enterprise deal

    A customer asked for a recent pentest report

    The security questionnaire has a line for it and the deal waits on it. You get a scoped test, a report written for their security team, and a signed letter to attach.

  3. 03 · Before launch

    A new app about to meet real users

    Test the web app, the mobile app and the API behind them before the first real customer does. Cheaper to fix now than after the first incident.

  4. 04 · Compliance

    An audit or standard that expects testing

    PCI DSS requires regular penetration testing, and SOC 2 and ISO 27001 auditors commonly ask to see it. The report and the retest give them the evidence.

    See our compliance engineering practice
  5. 05 · After a change

    A major release, migration or new integration

    A new payment flow, a move to a new cloud account, a new single sign-on provider. Test what changed before it becomes the weakest part of the system.

Honest scope

Not a fit if…

If any of these describe you, we will say so on the scoping call and point you to a firm that fits better. The call is free either way.

  • Your regulator or customer requires a test from an accredited firm (CREST, or a regulator's own approved list). Tell us on the call and we will say plainly whether our report fits.
  • You want us to test software we built or audited for you and the reader needs independence. Then we scope the test for you and hand it to an outside firm.
  • You need a red team exercise, social engineering or physical testing. We test applications, networks and cloud, not people or buildings.
  • You want a clean report without fixing what we find. The retest and the letter reflect what is actually still open.

How we run a VAPT engagement.

Six steps from the first call to the signed letter. Testing never starts before the scope and your authorization are in writing.

  1. 01

    Scoping & authorization

    Targets, roles, test windows and exclusions agreed in writing, with your signed authorization to test. Nothing is touched before this exists.

  2. 02

    Recon & vulnerability assessment

    Mapping the attack surface, then automated scanning for coverage: exposed services, known vulnerabilities, weak configuration.

  3. 03

    Manual penetration testing

    Verifying what the scan found, then testing by hand what it cannot: access control, business logic, chained attacks. Critical findings are reported to you the same day.

  4. 04

    Report & readout

    The full report with CVSS scores, proof of concept and fixes, walked through on a call with your engineers so nothing is lost in the PDF.

  5. 05

    Retest

    Once your fixes are in, we test each finding again at no charge and reissue the report with its final status.

  6. 06

    Attestation

    A signed letter stating the scope, dates and outcome, ready for the customer, auditor or regulator who asked.

Common questions, answered.

  • What is VAPT?

    Vulnerability assessment and penetration testing. The vulnerability assessment scans the whole surface for known weaknesses. The penetration test is a person verifying those findings and trying to exploit the system by hand, including the access control and business logic flaws no scanner finds. Together they tell you what is exposed and what an attacker could actually do with it.

  • What does a VAPT engagement cost?

    Price varies with the scope of the work: how many applications, roles, API endpoints, hosts or cloud accounts are in it. Each engagement is fixed-price once the scope is agreed in writing, and the retest is included. The scoping call is free; you accept the quote or you do not.

  • Do you do the testing yourselves?

    Yes. Our own security team does the testing, from scoping to the signed letter. We do not resell or subcontract the test to another firm.

  • What do you test?

    Web applications and APIs, iOS and Android apps, external and internal networks and servers, and cloud configuration on AWS, Azure and Google Cloud. Each can be bought on its own or combined into one engagement.

  • Is the retest really free?

    Yes. Once your team has fixed the findings, we retest each one at no extra charge and reissue the report with every finding marked fixed or still open. The signed attestation letter reflects the retest result.

  • What is in the attestation letter?

    The scope that was tested, the test dates, the methodology, and the outcome after the retest, signed by IrenicTech. It is the document you hand to an enterprise customer, an auditor or a regulator who asked for proof of a recent test, without sharing the full report.

  • Will testing break production?

    We agree the test windows, rate limits and anything off limits before we start, and we prefer a staging environment that matches production when you have one. Destructive tests, such as denial of service, are never run unless you ask for them in writing.

  • Do your VAPT reports work for UAE regulators?

    UAE frameworks such as the UAE Information Assurance standard, the Dubai DESC Information Security Regulation and ADHICS expect regular VAPT. Tell us which framework applies and we scope and report against it. If a regulator requires a tester from its own approved list, we will tell you on the scoping call whether our report fits.

  • How often should we run a penetration test?

    At least once a year, and after any major change: a new release, a cloud migration, a new payment or sign-in flow. PCI DSS requires testing at least annually and after significant changes, and most enterprise customers ask for a report from the last twelve months.

  • Can you test an app you built for us?

    We can, but we cannot be independent of our own code. If the reader of the report needs independence, we scope the test, hand it to an outside firm, and fix what they find.

Start a conversation

Tell us what you’re building.

Share the essentials and we’ll reply within 4 hours with a real next step, not an auto-responder.

What happens next

  1. We reply within 4 hours, from a real person, not an auto-responder.
  2. A short scoping call to understand the goal, constraints, and timeline.
  3. A fixed-scope discovery sprint: a working prototype and a written estimate.
Office
Sharjah, United Arab Emirates
Hours
Sun–Thu · 9am–6pm GST

Fields marked are required. By sending you agree to our Privacy Policy.